Security Research · Redacted Case File · Remediation
Working on It
A public API key could write configurations, publish images under a trusted brand, and send official messages to arbitrary recipients. The report was triaged as High before lunch. Five months later, the most durable control was still the sentence “we are working on it.”
The short version
- Two identical API keys appeared in unrelated public code repositories
- The key was intentionally public; the dangerous part was its authority to read protected data, create objects, publish trusted content, and trigger branded email
- Every impact test used my own inbox, phone, and harmless content
- The report was accepted as High within three hours
- Five months of acknowledgements left a symptom-level image filter and rate limits attached to objects an unauthenticated caller could mint
- The image filter blocked what its decoder understood and allowed a phone-readable code its decoder did not
- Names, domains, keys, routes, identifiers, and live-target operational details are withheld
01The public secret
The story started with two API keys in two unrelated public repositories. They were live, identical in privilege, and sufficient to reach an API belonging to a household-name consumer brand.
Without a key, a protected request returned 403. With either key, the API returned planner data and product assets. It also accepted writes: new configurations, image uploads, and notification jobs. One chain ended with an email delivered to any supplied recipient from the brand’s official no-reply identity.
The report initially described leaked credentials. Engineering supplied an important correction:
“We designed this API key to be public. The problem may be the scope of the API key.”
Correct. That distinction makes the design worse, not safer.
If a credential is deliberately shipped to every browser, it is not authentication. It is a label. Every person on the internet possesses it by design. The only safe privileges behind that label are privileges the entire internet may exercise.
The secret was never the string. The secret was that possession of a public string meant permission to perform private actions.
02High before lunch
The report was submitted shortly after 09:30. Preliminary review passed eleven minutes later. By noon it was triaged, assigned to the responsible team, and scored High.
That part worked beautifully. The platform recognized the evidence, the impact chain was reproducible, and the severity reflected a network-reachable action requiring no user interaction or account.
Then time changed viscosity.
High severity accepted. Remediation begins.
The key is confirmed public by design. Excessive scope is identified as the real problem.
Engineering says the issue requires “a consequence of actions.”
“We are working on the fix.”
“Our teams are still working on this issue.”
The researcher is asked to validate a fix in the comment thread. No formal retest is opened.
API scoping is described as a complex change across several applications.
“Our teams are still working on this issue.”
The researcher is again asked to validate in comments. Again, no formal retest is opened.
The new image filter is bypassed during controlled validation.
Rate limits are shown not to constrain realistic pacing or object rotation.
The report acquired handlers faster than the credential lost powers.
03The button
Twice, the handling team asked me to validate the fix through ordinary comments. The platform has a formal retest workflow. The organization opens it, defines the request, and the researcher returns structured evidence through a dedicated form.
I asked them to use it. It was not a philosophical demand. It was two clicks and a record of what, exactly, was supposed to be fixed.
A formal retest creates a boundary between “please poke production again” and an authorized validation exercise. It gives the researcher a scope, gives the organization a result, and gives both sides an audit trail. Asking casually in a comment transfers all ambiguity to the person doing the testing.
04The fix photographs the symptom
The original impact demonstration used the public key to upload a harmless image to the brand’s trusted content domain. The same public capability could prepare and send an official email containing that content. SPF, DKIM, and DMARC all passed because the message really came from the brand’s infrastructure.
The image was a benign phishing simulation. It showed why trusted hosting plus trusted delivery matters even when the upload only accepts ordinary image formats. A recipient does not inspect the API authorization model. A recipient sees a familiar sender, a familiar domain, and a picture telling them what to do next.
Five months later, images containing machine-readable codes began failing during upload. The original proof image, which had remained public for months, disappeared in the same window. A content filter had arrived.
It was also aimed at the screenshot, not the authority that created the screenshot.
Detection is not decoding
I tested the filter with a small differential matrix. Normal codes were rejected. Rotated, mirrored, inverted, and low-contrast codes were also rejected when the server could decode them. Fake code-like geometry without a valid payload passed.
Then a deliberately degraded code passed. The server could no longer decode it, but a phone camera recovered it immediately. Embedded inside a normal banner, it was accepted, published under the trusted content domain, and remained scannable end to end.
| Question | Control | Failure |
|---|---|---|
| Can I read this code? | Decoder | Failure to read becomes permission to upload |
| Does this image contain code-like structure? | Detector | Can flag suspicious structure even when payload recovery fails |
| May this caller publish and notify? | Authorization | The question the image filter never asks |
The specimen below uses the same deterministic corruption routine as the controlled retest, with a new benign destination. It starts with an error-correction level H code and removes just over 20% of its original black pixels while preserving enough structure for a robust mobile decoder. Its only payload is https://saladin.su/.
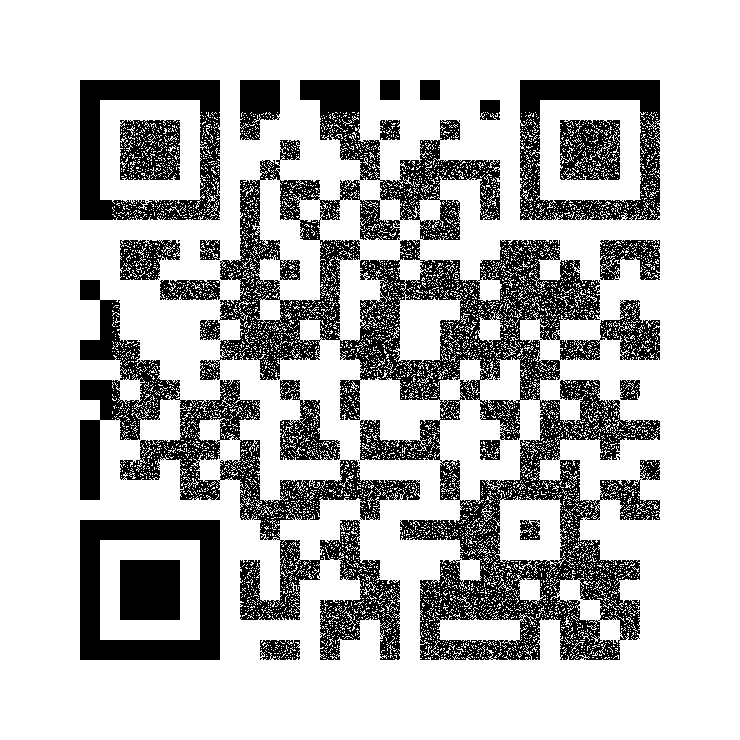
https://saladin.su/ at full and mobile display sizes. OpenCV returns no payload. Scan it yourself, or tap it for the original.The image makes the failure concrete: “my decoder failed” is not evidence that the input is safe. Different decoders have different recovery limits, and the attacker gets to choose the input between them.
Content inspection can be useful defense in depth. It cannot repair an authorization model that lets the anonymous public publish trusted content and distribute it through official channels.
05The decorative rate limit
The second visible control was throttling. In a tight loop, the service eventually returned 429. At natural request pacing, the bucket refilled quickly enough that the complete prepare-and-send cycle continued without meaningful resistance.
Another notification channel limited each configuration. Configurations, however, were unauthenticated to create. A fresh object produced a fresh quota bucket.
This is the rate-limit equivalent of issuing one parking ticket per car while handing out free cars beside the meter.
A useful abuse control must attach cost to something the attacker cannot mint freely. Depending on the system, that can include an authenticated principal, verified recipient, tenant budget, source reputation, global queue budget, or combinations of all five. An object identifier supplied by an unauthenticated object factory is not an identity.
06Four-ish people, zero ownership
By the five-month mark, the report had accumulated several handlers, external participants, reassignment events, status chases, fix-validation requests, and carefully polished acknowledgements.
It had passed through preliminary review, triage, engineering, remediation, validation, and multiple rounds of “thank you for your patience.” It had not passed through least privilege.
This is how a report can be assigned to a team and still belong to nobody. Every participant can be responsive. Every message can be polite. Every dashboard can remain green. The vulnerability survives because communication is being measured where closure should be.
“We are working on it” is a perfectly respectable sentence for a week. By month five, it is a monitoring metric.
The comedy is not that a fix took time. Splitting a public client credential from several applications can be real architecture work. The comedy is that the architecture work remained pending while two cheaper controls were shipped around the proof of concept, then handed back to the researcher as if regression testing were a community activity.
07What a root fix looks like
| Layer | Required property |
|---|---|
| Public client key | Read-only access to resources that are genuinely public |
| Configuration writes | Authenticated session, ownership checks, and per-principal quotas |
| Content publication | Authorization independent of file type or scanner verdict |
| Prepared messages | Bound to an authenticated owner, recipient, purpose, and short expiry |
| Notification sending | Rate limits at principal, recipient, tenant, source, and global levels |
| Content scanning | Detection as defense in depth, with suspicious decode failures handled safely |
| Validation | Formal retest with explicit acceptance criteria and one accountable owner |
Rotate the exposed keys, certainly, but rotation alone changes the public string without changing the public authority. If the new key returns to the same frontend with the same scopes, the remediation is a costume change.
08The finding behind the finding
The weakness label on the report said hard-coded credentials. Technically true, conceptually incomplete. The key was hard-coded because it was intended to be public. The actual bug was capability collapse: one client token represented browsing, writing, publishing, and sending.
The first remediation treated the malicious picture. The second treated request speed. Neither treated the caller’s authority.
Security programs love nouns: ticket, team, SLA, scanner, rate limiter, retest. Vulnerabilities live in verbs: read, create, publish, send. If an anonymous caller can still perform the dangerous verbs, the nouns are office furniture.
Working on it is a status. It is not a security control.
Disclosure note: the organization, product, handling parties, usernames, API keys, repositories, domains, routes, object identifiers, and recipients have been removed. All impact validation used addresses, devices, and harmless content controlled by the researcher. Live-target operational details remain withheld while remediation is incomplete.